Side A · Liner notes
How Quantum Computing Advances Are Altering the Landscape of Cryptography
Nutrition · Words by Craig Costello · Released
The threat from quantum computers to current cryptographic systems is more imminent than anticipated, bolstered by rapid algorithmic advancements and hardware improvements.
Online data security has long been considered a robust fortress, safeguarded by a combination of strong passwords and resilient encryption methods. For years, it's been said that even the most powerful supercomputers, working relentlessly for millennia, couldn't crack today's cryptography. However, recent developments in quantum computing suggest that this security may soon be within reach of these emerging technologies, leading experts to point to a critical juncture for cryptography, often referred to as “Q-Day.”
The advances in quantum computing are occurring on two main fronts: the development of hardware through major tech companies and the refinement of quantum algorithms. Tech giants like IBM and Google are in a fierce race to create larger and more powerful quantum computers. For instance, IBM's recent announcements indicate its ambitions to achieve a computational advantage over classical computers within specific applications by this year. More importantly, they're aiming for a "fault-tolerant" quantum system by 2029, which would represent a significant leap in computational capabilities.
On the algorithmic side, theorists are making strides that could significantly reduce the number of resources required to break existing cryptographic systems. Research has indicated that the resources needed to undermine current encryption may be much less than earlier estimates suggested. This merging of hardware and software improvements signals that the timeline for widespread quantum computing capabilities may be accelerating.
The Quantum Hardware Race
At the core of quantum computers are quantum bits, or qubits, which utilize the unique behaviors of quantum physics to execute computations in ways traditional binaries cannot match. The immediate goal in this field is to scale up the number of qubits so multiple can work together effectively. The greater the number of qubits that can be combined, the better these quantum machines should perform, leading what is called the "quantum advantage."
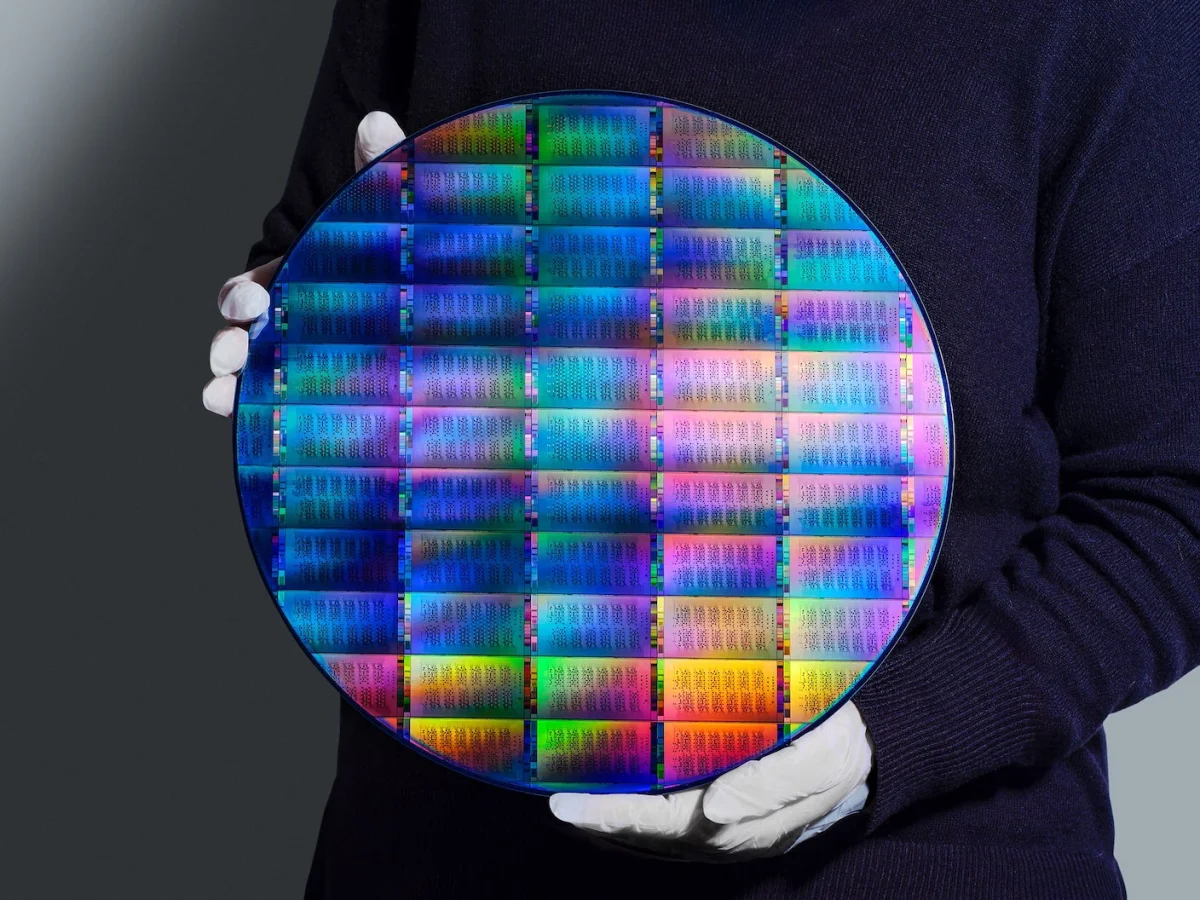
For example, late last year, IBM unveiled a 120-qubit chip, which they hope will demonstrate quantum advantage for specific tasks. Similarly, Google has announced a strategic shift towards adopting cryptographic techniques resistant to quantum attacks—this is often termed “post-quantum cryptography.” As the technology landscape transforms, companies like PsiQuantum are innovating, employing light-based qubits alongside traditional chip-manufacturing techniques, while other experimental platforms have successfully managed thousands of qubits in laboratory settings.
In light of these advancements, standards organizations are outlining explicit timelines to transition away from encryption methods vulnerable to quantum attacks. In the United States, the National Institute of Standards and Technology (NIST) has proposed a timeline for phasing out such cryptography by 2035. Australia is also pushing for similar measures, advising organizations to plan their migrations to post-quantum encryption systems by 2030.
Algorithms Enhance Cracking Efficiency
While hardware progress is significant, advancements in quantum algorithms play a pivotal role in maintaining momentum in quantum attacks. In 1994, Peter Shor’s discovery highlighted how quantum computers could significantly expedite finding prime factors, which is essential for breaking common encryption standards like RSA. For years, it was estimated that a quantum computer would require millions of physical qubits to pose a real threat—this made the potential risks feel far-off. However, that outlook is now changing.
In March, Google’s Quantum AI team released findings suggesting that far fewer resources might be needed to compromise elliptic curve encryption methods, which are employed by cryptocurrencies such as Bitcoin and Ethereum. They proposed that a quantum computer could potentially crack these systems with fewer than 500,000 physical qubits—substantially lower than previous estimates. Further research from a collaboration among institutions like Caltech and Berkeley indicates that Shor's algorithm could become feasible with as few as 10,000 to 20,000 atomic qubits.
This progressive reduction signifies that the efficiency of code-breaking capabilities is increasing. The developments in quantum algorithms alongside hardware improvements suggest that the barriers to executing quantum attacks are consistently diminishing, even before extensive quantum hardware becomes widely deployed.
What Lies Ahead?
The implications of these findings are profound. Though there is currently no immediate threat that existing encryption systems will be compromised overnight, the trajectory of developments points towards a future where traditional cryptographic methods may be insufficient. Each technological improvement shortens the timeline for quantum capabilities to surpass current defenses.
Fortunately, proactive measures already exist. NIST has approved several post-quantum cryptographic algorithms believed to be resistant to quantum threats. Tech companies are beginning to deploy these approaches in hybrid models—Google Chrome and Cloudflare already have some level of post-quantum protective measures in their services.
As systems dependent on elliptic-curve cryptography face particular vulnerabilities, especially in sectors like cryptocurrency and secure communication, addressing these potential weaknesses is critical. The focus must also remain on observing developments not only in quantum hardware but also in algorithms and error correction methods, as recent results show these advancements could have a significant impact on the estimated resources needed for successful quantum attacks.
As headlines continue to emerge detailing reduced qubit requirements and advancements in quantum algorithms, it’s imperative to recognize these as incremental steps towards a reality where existing cryptographic safeguards may soon be inadequate. The pathway forward is clear: transitioning to quantum-safe cryptography should be a matter of urgency and diligence.
This article is republished from The Conversation under a Creative Commons license. Read the original article.